

Cloudflare DNS vs Amazon Route 53 for Email: 2027 Propagation Speed, DNSSEC & API Automation
Published by Fred Dawson • Senior Deliverability Systems Architect • 19 min read
Email deliverability depends on authoritative DNS performance. When destination Mail Transfer Agents (Gmail, Microsoft 365, Yahoo) receive an incoming SMTP connection, their MX daemons immediately query the sender’s domain for SPF TXT records, 2048-bit DKIM public keys, DMARC policies, and BIMI assertions. If authoritative DNS queries timeout or fail to propagate, legitimate messages are deferred or dropped into spam. This guide benchmarks the two leading authoritative Anycast cloud providers: Cloudflare DNS and Amazon Route 53, analyzing propagation latency, DNSSEC ergonomics, API provisioning, and the infamous “Orange Cloud” mail routing pitfall.
1. Anycast Propagation Speed & Global Edge Density
When updating email authentication records—such as rotating a 2048-bit DKIM selector key or tightening a DMARC policy from p=none to p=reject—propagation speed across destination ISP resolvers is critical.
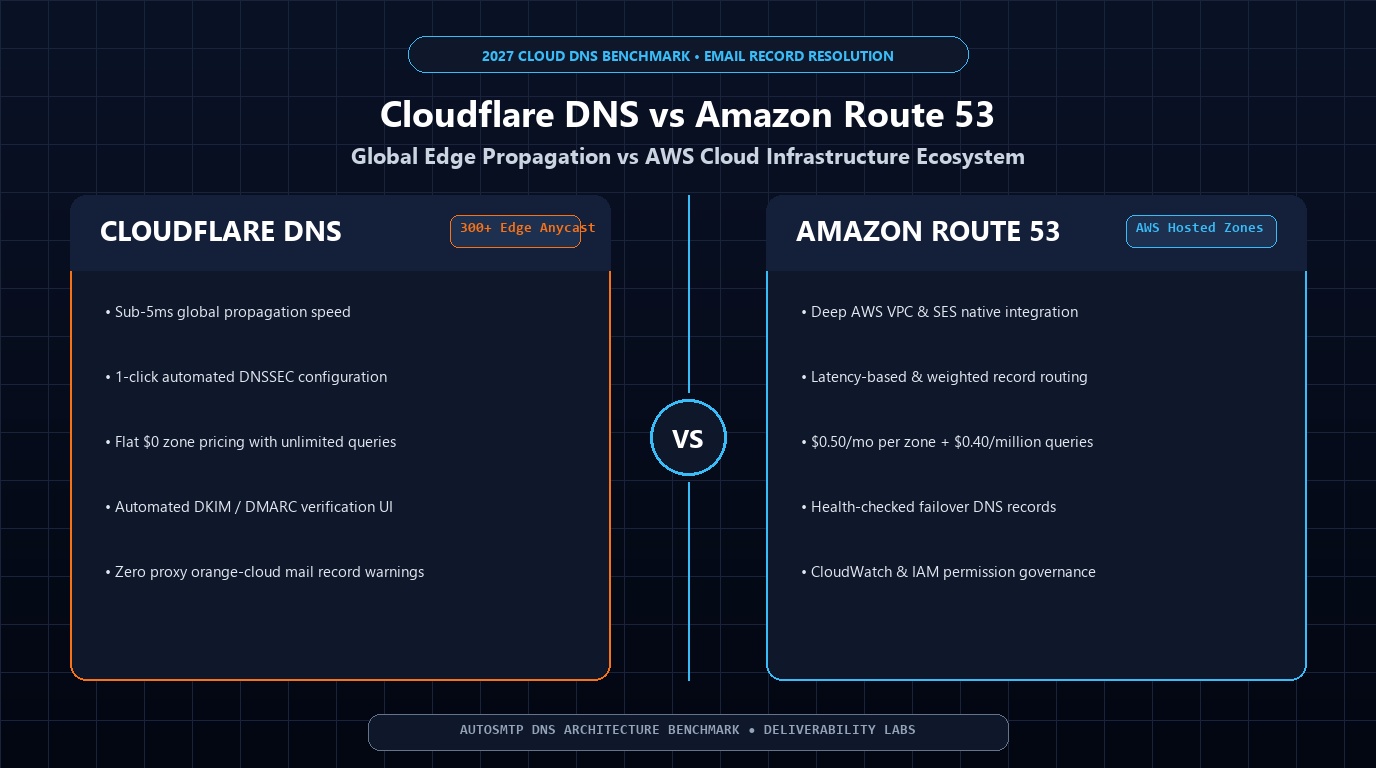
Cloudflare DNS: Operates an Anycast network spanning over 330 cities globally. When an administrator updates a TXT record via the Cloudflare dashboard or API, the change propagates across Cloudflare’s entire global edge in less than 5 seconds. Destination resolvers querying Cloudflare nameservers receive the updated record almost instantaneously once their local TTL expires.
Amazon Route 53: Operates an enterprise Anycast network across AWS edge locations. While highly reliable with a 100% availability SLA, Route 53’s control plane uses eventual consistency across its four assigned nameserver delegations (e.g., ns-xxxx.awsdns-xx.com). Record updates typically require 30 to 60 seconds to synchronize across all global authoritative nameservers.
2. The “Orange Cloud” Proxy Pitfall in Email Routing
The single most common operational error encountered by deliverability engineers on Cloudflare is inadvertently proxying email hostnames through Cloudflare’s HTTP CDN (the “Orange Cloud” setting):
The Orange Cloud Trap (Port 25 Failure)
Cloudflare’s core reverse-proxy only inspects and routes HTTP/HTTPS web traffic (ports 80, 443). If an operator sets an A record for mail.domain.com or smtp.domain.com to “Proxied” (Orange Cloud), Cloudflare intercepts incoming connections and drops all non-HTTP packets. Destination MTAs attempting to deliver email on TCP port 25 fail with Connection refused or timeout errors, instantly breaking incoming mail flow.
DNS-Only (Grey Cloud) Best Practice
All records associated with mail delivery—including A records for mail servers, MX records, and TXT records for SPF, DKIM, and DMARC—must be strictly configured as DNS-Only (Grey Cloud). Cloudflare’s modern dashboard includes automated warnings flagging proxied records that match MX target hostnames.
# Incorrect: Hostname resolves to Cloudflare Anycast HTTP CDN IPs (104.21.x.x / 172.67.x.x)
dig +short mail.example.com
104.21.48.12
172.67.182.44  <-- ERROR: Cloudflare HTTP Proxy active! Port 25 will be dropped!

# Correct: Hostname resolves directly to dedicated bare-metal server IP (Grey Cloud)
dig +short mail.example.com
198.51.100.25  <-- Direct origin server IP. Port 25 open and ready for SMTP delivery!
3. DNSSEC Implementation: Automated vs Manual KMS
DNS Security Extensions (DNSSEC) protect against DNS spoofing and cache poisoning by cryptographically signing DNS records. With major ISPs (especially in Europe and government sectors) enforcing DANE (RFC 7672) and strict DNSSEC validation, deploying DNSSEC is mandatory for top-tier deliverability.
- Cloudflare DNS: Provides 1-click automated DNSSEC. Cloudflare automatically generates the Key Signing Key (KSK) and Zone Signing Key (ZSK), signs all zone records dynamically on-the-fly, and automatically rotates ZSKs every 30 days. Operators simply copy the generated DS record into their domain registrar.
- Amazon Route 53: While Route 53 supports DNSSEC, configuration requires enabling DNSSEC signing in Route 53, creating an asymmetric customer managed key (CMK) in AWS Key Management Service (KMS), and manually managing key rotation schedules.
4. Terraform & API Automation for Multi-Domain Fleets
When operating large-scale multi-domain cold email or outbound marketing infrastructure (managing 100 to 1,000+ domains), programmatic record provisioning is essential:
Cloudflare: Extremely developer-friendly REST API (POST /client/v4/zones/{zone_id}/dns_records). Furthermore, Cloudflare allows unlimited free zones on its standard plan with zero query surcharges, making it virtually free to manage hundreds of sending domains.
Route 53: Imposes a flat fee of $0.50 per hosted zone per month for the first 25 zones ($0.10/zone thereafter), plus $0.40 per million DNS queries. For an enterprise running 500 sending domains processing 100M DNS queries monthly, Route 53 adds over $90/month in recurring DNS taxes for identical record publishing.
5. Cloudflare vs Route 53 Technical Matrix
| Architectural Pillar | Cloudflare DNS | Amazon Route 53 | Deliverability Recommendation |
|---|---|---|---|
| Global Propagation Time | Sub-5 seconds across 330+ Anycast cities | 30 - 60 seconds across AWS nameservers | Cloudflare: Instant SPF/DKIM record updates |
| Pricing Structure | 100% Free authoritative DNS (Unlimited queries) | $0.50/mo per zone + $0.40/M queries | Cloudflare: Dramatic savings for multi-domain fleets |
| DNSSEC Management | 1-Click automated signing & key rotation | Requires AWS KMS CMK key setup & maintenance | Cloudflare: Zero-maintenance cryptographic signing |
| Traffic Routing Capabilities | Basic geo-steering / load balancing (Paid add-on) | Latency-based, weighted, and failover routing | Route 53: Superior for complex AWS multi-region failover |
| Email-Specific UI Guards | Built-in warnings for proxied mail records | None; raw DNS management only | Cloudflare: Prevents catastrophic Orange Cloud outages |
How a Deliverability Agency Cut DKIM Rotation Windows from 48h to 5s
A cold outbound agency managing 450 customer domains was experiencing periodic deliverability drops when rotating 2048-bit DKIM selector keys. Because domains were hosted across fragmented registrar nameservers with 24-hour TTL caching, destination MTAs failed cryptographic signature validation during rotation transitions. By migrating all 450 domains to Cloudflare DNS via automated Terraform scripts, DKIM rotation propagation dropped to under 5 seconds globally, eliminating DKIM failure deferrals and saving $225/month in hosted zone fees compared to Route 53.
The AutoSMTP Deliverability Defense Advantage
Inbound and outbound filtering pipelines require robust underlying transport hardware. AutoSMTP provisions sovereign, dedicated bare-metal MTA infrastructure engineered for high-throughput filtering, synchronous 550 bounce suppression, and permanent reputation control.
Provisions fully licensed PowerMTA and KumoMTA clusters on enterprise bare-metal with dedicated IPv4 subnets and predictable flat pricing.
Monitors Google Postmaster spam ratios (<0.1%) and real-time ISP deferrals with algorithmic volume scaling across your entire IP pool.
RFC 5321 in-band 550 bounce suppression, automated Yahoo/Outlook Complaint Feedback Loops (CFL), and instant bad-IP eviction.
Pre-configured forward and reverse DNS (PTR) per IP, SPF CIDR alignment, 2048-bit DKIM rotation, and strict DMARC enforcement.
Upgrade Your Email Infrastructure with Dedicated Bare Metal
Eliminate filter lag, queue serialization bottlenecks, and noisy neighbor contamination. Deploy a turnkey AutoSMTP cluster today.
Deploy Turnkey MTA Cluster →