

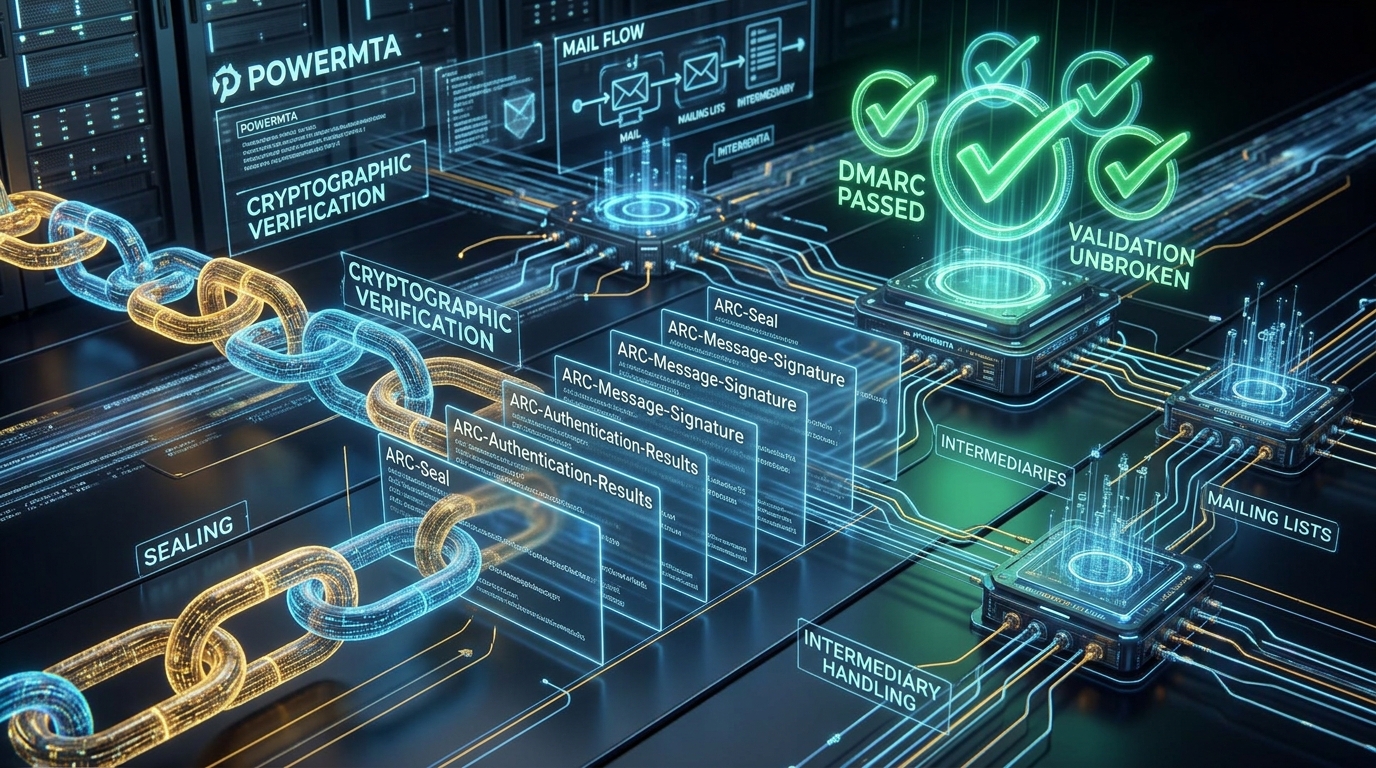
PowerMTA ARC Signing Guide: RFC 8617 Authenticated Received Chain & 2027 Forwarding Standards
Published by Fred Dawson • Senior Deliverability Systems Architect • 19 min read
When email travels through intermediate hops—such as corporate mailing lists, security filtering appliances (Proofpoint, Mimecast), or automated CRM forwarding relays—headers and body content are frequently altered (e.g., adding subject tags like [Team-Discussion] or injecting footer disclaimers). These benign modifications break the original sender’s DKIM (RFC 6376) signature, while the forwarder’s IP address fails SPF (RFC 7208). If the author domain publishes a strict DMARC policy (p=reject), receiving mailbox providers (Gmail, Outlook) are forced to reject the legitimate message. Authenticated Received Chain (ARC, RFC 8617) preserves the original authentication state by creating an unbroken cryptographic chain of custody. This guide delivers a hands-on implementation blueprint for configuring ARC signing, DNS selector publishing, and inbound chain evaluation in PowerMTA.
- 1. The Indirect Mail Crisis: Why Intermediaries Break DMARC
- 2. Anatomy of the Three ARC Headers: AAR, AMS, and AS
- 3. Generating 2048-Bit ARC Keys & DNS Selector Records
- 4. PowerMTA ARC Directives: Inbound Verification & Outbound Signing
- 5. The 2026/2027 IETF Landscape: ARC Limitations & DMARCbis
- 6. Email Authentication Preservation Matrix
- 7. Production Case Study: Mailing List Deliverability Overhaul
- 8. The AutoSMTP Deliverability Defense Advantage
1. The Indirect Mail Crisis: Why Intermediaries Break DMARC
Under DMARC (RFC 7489), an email is considered legitimate only if either SPF or DKIM passes in direct domain alignment with the RFC 5322 From: header. This security model functions seamlessly for direct point-to-point mail delivery.
However, when a message traverses an indirect email intermediary:
- SPF Alignment Breaks: The intermediate server connects to the final recipient from its own IP address, which is not authorized in the original sender’s SPF record.
- DKIM Alignment Breaks: If the intermediary modifies the message—such as appending an unsubscribe link, reformatting MIME parts, or altering subject lines—the cryptographic body hash (
bh=) or header signature (b=) fails validation.
When both SPF and DKIM fail, a sender with p=reject will have their email dropped by Gmail, Yahoo, and Outlook. ARC solves this by allowing each intermediate hop to record the authentication status it observed upon receipt and sign that assessment with its own cryptographic key before forwarding.
2. Anatomy of the Three ARC Headers: AAR, AMS, and AS
ARC introduces a sequence of three ordered, indexed headers (where i=1 represents the first intermediary, i=2 the second, and so on):
# 1. ARC-Authentication-Results (AAR)
# Records the authentication validation results observed when the intermediary received the email
ARC-Authentication-Results: i=1; mx.intermediary.com;
    dkim=pass header.i=@sender.com header.s=s2026 header.b=Ab12Cd34;
    spf=pass (mx.intermediary.com: domain of alice@sender.com designates 192.0.2.1 as permitted sender) smtp.mailfrom=alice@sender.com;
    dmarc=pass (p=reject sp=reject dis=none) header.from=sender.com

# 2. ARC-Message-Signature (AMS)
# A DKIM-style signature over the message headers and body as modified by the intermediary
ARC-Message-Signature: i=1; a=rsa-sha256; c=relaxed/relaxed; d=intermediary.com;
    s=arc2026; t=1761148800;
    h=to:subject:message-id:date:from:mime-version:arc-authentication-results;
    bh=wX892jklSD8923KLJsd923kjsd8=;
    b=KLJds923...[base64 signature]...

# 3. ARC-Seal (AS)
# Seals the entire preceding ARC chain, validating that intermediate headers were not tampered with
ARC-Seal: i=1; a=rsa-sha256; d=intermediary.com; s=arc2026; t=1761148800; cv=none;
    b=Xyz8923...[base64 seal]...
The cv= (Chain Validation) tag indicates the integrity of previous ARC seals: cv=none for the first intermediary, and cv=pass for subsequent intermediaries that verified previous hops.
3. Generating 2048-Bit ARC Keys & DNS Selector Records
ARC signing requires an RSA private key on your PowerMTA server and a corresponding public key published in DNS:
# 1. Generate 2048-bit RSA Private Key for ARC
openssl genrsa -out /etc/pmta/arc2026.key 2048

# 2. Extract Public Key
openssl rsa -in /etc/pmta/arc2026.key -pubout -out /etc/pmta/arc2026.pub

# 3. Set Secure File Permissions
chown pmta:pmta /etc/pmta/arc2026.key /etc/pmta/arc2026.pub
chmod 0600 /etc/pmta/arc2026.key
Publish the public key in your authoritative DNS zone using the _domainkey namespace:
arc2026._domainkey.intermediary.com. IN TXT "v=DKIM1; k=rsa; p=MIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEA..."
4. PowerMTA ARC Directives: Inbound Verification & Outbound Signing
Incorporate the following directives into your PowerMTA configuration to handle both inbound chain verification and outbound ARC signing:
# ==============================================================================
# RFC 8617 AUTHENTICATED RECEIVED CHAIN (ARC) CONFIGURATION
# ==============================================================================

# 1. Inbound ARC Verification
# Evaluates incoming ARC chains from upstream senders on all MX listeners
arc-verify yes

# 2. Outbound ARC Signing Pool
<virtual-mta vmta-arc-forwarder>
    smtp-source-ip 198.51.100.55
    host-name mail.intermediary.com

    # Enable ARC signing on forwarded messages
    arc-sign yes

    # Path to cryptographic private key
    arc-key /etc/pmta/arc2026.key

    # DNS selector and signing domain
    arc-selector arc2026
    arc-domain intermediary.com

    # Canonicalization algorithms (relaxed headers / relaxed body)
    arc-canonicalization relaxed/relaxed
</virtual-mta>
5. The 2026/2027 IETF Landscape: ARC Limitations & DMARCbis
While ARC successfully enables major mailbox providers (Gmail, Microsoft, Fastmail) to accept forwarded mail that would otherwise fail DMARC, operators must understand its evolving governance in 2026/2027:
- Reputation Dependency: ARC does not automatically force a mailbox provider to trust an intermediate forwarder. Recipient servers maintain local reputation scores for ARC sealers. If an intermediate forwarder seals spam or phishing traffic, its ARC signatures are ignored.
- DMARCbis (RFC 7489bis): The IETF DMARC working group has actively drafted updates addressing indirect mail flows, clarifying how receivers should interpret ARC chains alongside Sender Rewriting Scheme (SRS).
- Best Practice Recommendation: For bulletproof inbox placement across both consumer and enterprise destinations, deploy ARC signing alongside SRS. SRS guarantees that SPF passes on the forwarder’s return-path, while ARC guarantees that the original DKIM/DMARC pass is cryptographically asserted for receivers that evaluate ARC.
6. Email Authentication Preservation Matrix
| Standard | What It Validates | Survives Forwarding | Survives Body Modification | Primary Use Case |
|---|---|---|---|---|
| SPF (RFC 7208) | Connecting IP vs Domain TXT | No (Breaks immediately) | Yes (Headers only) | Direct sender authorization |
| DKIM (RFC 6376) | Cryptographic Body & Header Hash | Yes (If unedited) | No (Hash mismatch) | Message integrity & origin |
| DMARC (RFC 7489) | SPF/DKIM Alignment with From: | No (If either breaks) | No (If DKIM breaks) | Domain anti-spoofing policy |
| SRS | Envelope Return-Path (MAIL FROM) | Yes (Rewrites Return-Path) | Yes | SPF preservation on forwarders |
| ARC (RFC 8617) | Cryptographic Chain of Authentication | Yes (Seals prior auth state) | Yes (Allows benign edits) | Intermediaries & mailing lists |
Case Study: Restoring Deliverability for a 500,000-Subscriber Technical Mailing List
An open-source developer mailing list operating on Mailman and PowerMTA experienced widespread delivery drops following corporate adoption of strict p=reject DMARC policies. Because the mailing list software appended [Dev-List] to subject lines and inserted an unsubscribe footer, DKIM signatures from corporate contributors (e.g. @company.com) failed, resulting in automated 550 rejections at Gmail and Microsoft.
The team deployed a 2048-bit ARC signing pipeline on their PowerMTA relay nodes. When PowerMTA ingested the original email, it verified the initial DKIM pass, appended the ARC-Authentication-Results, ARC-Message-Signature, and ARC-Seal headers, and dispatched the modified message to subscribers. Google Workspace and Microsoft 365 servers recognized the trusted ARC seal, verified the original author pass, and delivered 100% of list communications directly to subscriber inboxes.
The AutoSMTP Deliverability Defense Advantage
Inbound and outbound filtering pipelines require robust underlying transport hardware. AutoSMTP provisions sovereign, dedicated bare-metal MTA infrastructure engineered for high-throughput filtering, synchronous 550 bounce suppression, and permanent reputation control.
Provisions fully licensed PowerMTA and KumoMTA clusters on enterprise bare-metal with dedicated IPv4 subnets and predictable flat pricing.
Monitors Google Postmaster spam ratios (<0.1%) and real-time ISP deferrals with algorithmic volume scaling across your entire IP pool.
RFC 5321 in-band 550 bounce suppression, automated Yahoo/Outlook Complaint Feedback Loops (CFL), and instant bad-IP eviction.
Pre-configured forward and reverse DNS (PTR) per IP, SPF CIDR alignment, 2048-bit DKIM rotation, and strict DMARC enforcement.
Upgrade Your Email Infrastructure with Dedicated Bare Metal
Eliminate filter lag, queue serialization bottlenecks, and noisy neighbor contamination. Deploy a turnkey AutoSMTP cluster today.
Deploy Turnkey MTA Cluster →